Sabtu, 08 Juli 2017

Step Past Times Pace Deed Lvm ( Vg-Volume Grouping , Pv-Physical Voulme As Well As Lv- Logical Volume) To Approximately Other Linux Organisation

LVM Move: - We tin motility entire LVM Volume grouping to approximately other Linux System. 
It may require when yous are going to upgrade your electrical flow OS to the latest or at that spot is approximately lawsuit alongside electrical flow Server hardware or going to role novel server hardware.


Why Move LVM: -
1- There is approximately hardware lawsuit alongside electrical flow server
2- We convey novel Server hardware
3- Current OS is onetime version

Prerequisites:- 
1- Influenza A virus subtype H5N1 user alongside sudoers access over onetime System
2- user alongside sudoers privileges over novel System
Move LVM: - We need to perform next steps to motility LVM

My Current scenario as follows:
VG Name:  VG01


PV Name:  /dev/sdb1 in addition to /dev/sdc1 


LV Name:  LV01 in addition to LV02 


 Note: -first, brand certain no i is accessing the file on the active book inwards the book grouping nosotros are going to move.
Step 1: -  Unmount LV logical volume
Before, nosotros commence moving LVM necessitate to unmount let's role below ascendence to unmount LV
root@Server16: # umount /mnt/FLV
Step 2: - Make VG inactive 
Now nosotros necessitate to brand VG inactive, role below command.
root@Server16: # vgchange -a n VG01 
Step 3: - Export Volume Group
root@Server16: # vgexport VG01 Volume grouping VG01 is exported Cannot procedure book grouping VG01
After exporting VG, the Physical Volume volition exhibit upward equally beingness exported book grouping when yous volition execute command pvscan.


Step 4: - Shutdown System in addition to unplugged disk
After System Shutdown unplugged both the disk. Let's role init 0 ascendence to shutdown system.

Step 5: - Plugged disk to novel organization in addition to ability it on 
After putting both the disk to the novel system, I am going to ability it on in addition to volition exhibit yous how to import Volume Group.
Disk , VG in addition to LV details equally follows:


Step 6: - VG Import 
After putting all the disk to novel organization nosotros necessitate to import Volume Group, let's role below ascendence to Import VG using ascendence vgimport

root@US16: # vgimport VG01   Volume grouping "VG01" successfully imported 

Step 7: - Activate Volume Group
After successful import of VG, We necessitate to active Volume Group using ascendence below
root@US16: # vgchange -a y VG01   ii logical volume(s) inwards book grouping "VG01" instantly active
Step 8: - Create mountain point 
Now Volume Group has successfully import in addition to activated, let's practise mountain betoken then nosotros tin mountain in addition to commence using Logical Volume.
root@US16: # mkdir /mnt/lvm1 root@US16: # mkdir /mnt/lvm2 
Mount betoken successfully created.
Step 9: - Mount Logical Volume
root@US16: # mount /dev/VG01/LV01 /mnt/lvm1/ 
Step 10:  Check onetime information of LV01 Logical Volume
Volume Group Import has done successfully, in addition to Logical Volume mounted equally well.
let's cheque existing information inwards the mounted LV.


Volume Group has successfully Imported to novel organization in addition to working equally expected. We tin brand fstab entry to mountain Logical Volume permanently.
Step 11: - Make Fstab entry to mountain LV permanently
Let's role below ascendence to mountain it permanently.
root@US16: # vi /etc/fstab
Append trouble below inwards the goal of fstab file
/dev/VG01/LV01  /mnt/lvm1       ext4    errors=remount-ro 0     0
Your fstab file looks similar below


Step 12: - Use ascendence mountain -a to apply changes
After making alter inwards fstab file nosotros necessitate to restart organization to apply changes, merely nosotros tin role ascendence mountain -a to apply changes without restart system.
root@US16: # mount -a
Logical Volume has been successfully mounted permanently.

!!!That's all close VG Moving!!!! Thank yous then much for reading.


Sumber https://linuxhowtoguide.blogspot.com/

Jumat, 24 Maret 2017

How To Install As Well As Configure Pnp4nagios Bulk+Npcd Trend Amongst Nagios4.X Centos 7.X

PNP4NAGIOS:-

Pnp4Nagios plant alongside Nagios to generate the graph of services that are beingness monitored yesteryear Nagios server. With the handle of Pnp4Nagios, nosotros tin meet the graph anytime whenever needed,  It tape graph for all the configured services, We tin sentiment usage similar CPU, RAM, Disk Space etc.

Prerequisites:  

1- RRDTOOL, rrdtool-perl
2- Perl
3- Php-gd
4- perl-time-HiRes

Step 1-  Installation
To Install prerequisites run below command
[root@localhost  ]# yum install rrdtool perl-Time-HiRes rrdtool-perl php-gd

Once prerequisites installation done, download pnp4nagios.
Step 2- Download PNP4Nagios, Extract in addition to Install
[root@localhost  ]# wget https://sourceforge.net/projects/pnp4nagios/files/PNP-0.6/pnp4nagios-0.6.25.tar.gz
Once download transcend finished, extract packet using ascendancy below
[root@localhost  ]# tar zxfv pnp4nagios-0.6.25.tar.gz
Go to the Extracted directory in addition to configure it.
[root@localhost  ]# cd pnp4nagios-0.6.25
Configure pnp4nagios in addition to install using ascendancy below
[root@localhost pnp4nagios]# ./configure [root@localhost pnp4nagios]# brand all [root@localhost pnp4nagios]# brand fullinstall

Enable NPCD service to starting fourth dimension at kick fourth dimension in addition to starting fourth dimension it now.
[root@localhost  ]# chkconfig --add npcd && chkconfig --level 35 npcd on

Let's reboot httpd service.
[root@localhost  ]# systemctl restart httpd

Step 2- Let's depository fiscal establishment lucifer PNP4Nagios installation.

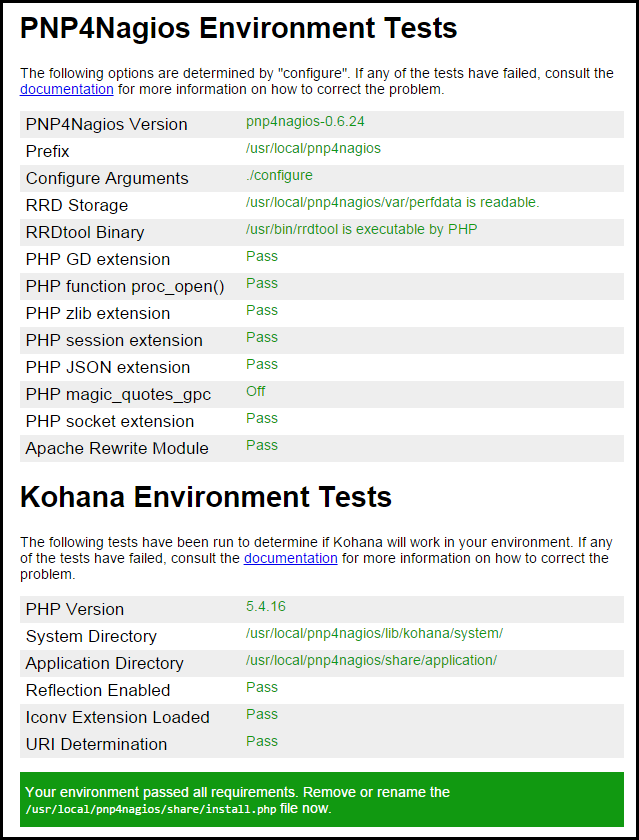
Open browser in addition to type URL:- 192.168.102.11/pnp4nagios/


After successful PNP4Nagios installation, you lot volition transcend the window similar above.

Step 3- Let's rename install.php to install.php-bak
[root@localhost  ]# mv  /usr/local/pnp4nagios/share/install.php /usr/local/pnp4nagios/share/install.php-bak

Step 4-  Make the required changes inward Nagios configuration to integrate PNP4Nagios to generate graph.

Make the changes inward nagios.cfg configuration file.
[root@localhost  ]# vi /usr/local/nagios/etc/nagios.cfg
Change the Process_performance_data=1 in addition to append below mentions line.
# Bulk / NPCD mode process_performance_data=1 service_perfdata_file=/usr/local/pnp4nagios/var/service-perfdata service_perfdata_file_template=DATATYPE::SERVICEPERFDATA\tTIMET::$TIMET$\tHOSTNAME::$HOSTNAME$\tSERVICEDESC::$SERVICEDESC$\tSERVICEPERFDATA::$SERVICEPERFDATA$\tSERVICECH$ service_perfdata_file_mode=a service_perfdata_file_processing_interval=15 service_perfdata_file_processing_command=process-service-perfdata-file  host_perfdata_file=/usr/local/pnp4nagios/var/host-perfdata host_perfdata_file_template=DATATYPE::HOSTPERFDATA\tTIMET::$TIMET$\tHOSTNAME::$HOSTNAME$\tHOSTPERFDATA::$HOSTPERFDATA$\tHOSTCHECKCOMMAND::$HOSTCHECKCOMMAND$\tHOSTSTATE::$ host_perfdata_file_mode=a host_perfdata_file_processing_interval=15 host_perfdata_file_processing_command=process-host-perfdata-file
Save in addition to leave of absence from file.
Now brand the required changes inward command.cfg file
[root@localhost  ]# vi /usr/local/nagios/etc/objects/commands.cfg
Go to the terminate of file in addition to append the crimson business below in addition to comment all the dark line.
# 'process-host-perfdata' ascendancy Definition #define command{ #       command_name    process-host-perfdata #       command_line    /usr/bin/printf "%b" "$LASTHOSTCHECK$\t$HOSTNAME$\t$HOSTSTATE$\t$HOSTATTEMPT$\t$HOSTSTATETYPE$\t$HOSTEXECUTIONTIME$\t$HOSTOUTPUT$\t$HOSTPERFDATA$\n" >> /usr/local/nagios/var/host-perfdata.out #       }   # 'process-service-perfdata' ascendancy Definition #define command{ #       command_name    process-service-perfdata #       command_line    /usr/bin/printf "%b" "$LASTSERVICECHECK$\t$HOSTNAME$\t$SERVICEDESC$\t$SERVICESTATE$\t$SERVICEATTEMPT$\t$SERVICESTATETYPE$\t$SERVICEEXECUTIONTIME$\t$SERVICELATENCY$\t$SERVICEOUTPUT$\t$SERVICEPERFDATA$\n" >> /usr/local/nagios/var/service-perfdata.out #       }  # 'process-host-perfdata' ascendancy Definition define command{ command_name process-host-perfdata command_line /usr/bin/printf "%b" "$LASTHOSTCHECK$\t$HOSTNAME$\t$HOSTSTATE$\t$HOSTATTEMPT$\t$HOSTSTATETYPE$\t$HOSTEXECUTIONTIME$\t$HOSTOUTPUT$\t$HOSTPERFDATA$$ }  # 'process-service-perfdata' ascendancy Definition define command{ command_name process-service-perfdata command_line /usr/bin/printf "%b" "$LASTSERVICECHECK$\t$HOSTNAME$\t$SERVICEDESC$\t$SERVICESTATE$\t$SERVICEATTEMPT$\t$SERVICESTATETYPE$\t$SERVICEEXECUTIONTIME$$ }  define command{ command_name process-service-perfdata-file command_line /bin/mv /usr/local/pnp4nagios/var/service-perfdata /usr/local/pnp4nagios/var/spool/service-perfdata.$TIMET$ }  define command{ command_name process-host-perfdata-file command_line /bin/mv /usr/local/pnp4nagios/var/host-perfdata /usr/local/pnp4nagios/var/spool/host-perfdata.$TIMET$ }   

Let's brand alter inward template.cfg file 
[root@localhost  ]# vi /usr/local/nagios/etc/objects/templates.cfg
Append the crimson business inward the below of file.
# PNP4NAGIOS # define host { hollo host-pnp action_url /pnp4nagios/index.php/graph?host=$HOSTNAME$&srv=_HOST_' class='tips' rel='/pnp4nagios/index.php/popup?host=$HOSTNAME$&srv=_HOST_ register 0 }  define service { hollo srv-pnp action_url /pnp4nagios/index.php/graph?host=$HOSTNAME$&srv=$SERVICEDESC$' class='tips' rel='/pnp4nagios/index.php/popup?host=$HOSTNAME$&srv=$SERVICEDESC$ register 0 
Save in addition to Exit from file

Now brand the alter inward the host configuration fiel
[root@localhost  ]# vi /usr/local/nagios/etc/objects/localhost.cfg

Append the next lines inward the terminate of file.
# Define a host for the local machine  define host{         purpose                     linux-server,host-pnp            ; Name of host template to purpose                                                         ; This host Definition volition inherit all variables that are defined                                                         ; inward (or inherited by) the linux-server host template definition.         host_name               localhost         alias                   localhost         address                 127.0.0.1         } 

# Define a service to "ping" the local machine
define service{
        purpose                             local-service,srv-pnp         ; Name of service template to use
        host_name                       localhost
        service_description             PING
        check_command                   check_ping!100.0,20%!500.0,60%
        }
Save in addition to leave of absence from file.

All the configuration changed completed successfully.

Step 5-  Now restart httpd, Nagios in addition to Npcd service using ascendancy below.
[root@localhost  ]# systemctl restart httpd && systemctl restart nagios && systemctl restart npcd

Step 6- Verify integration of PNP4Nagios

Open Nagios server URL:-  http://192.168.102.11/nagios/

After successful integration of PNP4nagios you lot transcend a graph symbol for each service similar inward below image:


And you lot volition meet graph for private service icon similar below:


Congratulation!!! Installation in addition to Integration of PNP4Nagios alongside Nagios server completed successfully done alongside Bulk+NPCD mode.


Sumber https://linuxhowtoguide.blogspot.com/

Jumat, 17 Maret 2017

How To Install Nagios 3.X On Centos 6.7 End Release

What Is Nagios Core:-

Nagios Core is an Open Source organization together with network monitoring application. It watches hosts together with services that yous specify, alerting yous when things become bad together with when they instruct better.

System Requirments:-

1- Linux machine (In my illustration I am using Centos 6.7)
2- HTTPd, PHP amongst gd together with CGI.

Nagios Installation:-

 Step 1- 
Add repository showtime to install Nagios
[root@odoo  ]# rpm -Uvh http://dl.fedoraproject.org/pub/epel/6/x86_64/epel-release-6-8.noarch.rpm Retrieving http://dl.fedoraproject.org/pub/epel/6/x86_64/epel-release-6-8.noarch.rpm warning: /var/tmp/rpm-tmp.2nIBRS: Header V3 RSA/SHA256 Signature, fundamental ID 0608b895: NOKEY Preparing...                ########################################### [100%]    1:epel-release           ########################################### [100%] [root@odoo  ]# 

[root@odoo  ]# rpm -Uvh http://rpms.famillecollet.com/enterprise/remi-release-6.rpm Retrieving http://rpms.famillecollet.com/enterprise/remi-release-6.rpm warning: /var/tmp/rpm-tmp.f5McIF: Header V4 DSA/SHA1 Signature, fundamental ID 00f97f56: NOKEY Preparing...                ########################################### [100%]    1:remi-release           ########################################### [100%] 

 Step 2- Complete installation & configuration part:

Run yum update
[root@odoo  ]# yum update
Install HTTPd server
[root@odoo  ]# yum install httpd
Install PHP
[root@odoo  ]# yum install php php-cli php-gh php-common

Install Nagios
[root@odoo  ]# yum install nagios nagios-plugins-all nagios-plugins-nrpe nrpe
Check Nagios version
[root@odoo  ]# nagios -v
Enable httpd together with Nagios service to laid about car during organization boot or restart
[root@odoo  ]# chkconfig httpd on && chkconfig nagios on
Start httpd & Nagios service
[root@odoo  ]# service httpd laid about && service nagios start
Open Port fourscore through iptables
[root@odoo  ]# vi /etc/sysconfig/iptables
Modify config file similar below
# Firewall configuration written past times system-config-firewall # Manual customization of this file is non recommended. *filter :INPUT ACCEPT [0:0] :FORWARD ACCEPT [0:0] :OUTPUT ACCEPT [0:0] -A INPUT -m field --state ESTABLISHED,RELATED -j ACCEPT -A INPUT -p icmp -j ACCEPT -A INPUT -i lo -j ACCEPT -A INPUT -m field --state NEW -m tcp -p tcp --dport 22 -j ACCEPT -A INPUT -m field --state NEW -m tcp -p tcp --dport fourscore -j ACCEPT -A INPUT -j REJECT --reject-with icmp-host-prohibited -A FORWARD -j REJECT --reject-with icmp-host-prohibited COMMIT 

Save together with kicking the bucket from file & restart iptables service
[root@odoo  ]# service iptables restart
 Step 3- Setup Nagios login details
 Set Nagios user get upwards together with password
[root@odoo  ]# htpasswd -c /etc/nagios/passwd nagiosadmin New password: ******* Re-type novel password:  ****** Adding password for user nagiosadmin 

 Step 4- Validate authentication & installation.
Check Nagios login using URL below


After successful authentication, yous volition instruct the window similar below.


!!!!!!!! Installation of Nagios completed successfully !!!!!!!!


Sumber https://linuxhowtoguide.blogspot.com/

Kamis, 02 Februari 2017

How To Install As Well As Configure Magento Alongside Nginx Ubuntu 16.04 Lts

Magento:

Magento is the well-nigh pop content administration organisation for e-commerce websites. It is used past times small-scale businesses as well as large enterprise companies alike, as well as tin live enhanced past times thousands of extensions as well as themes. Magento uses the MySQL database system, the PHP programming language, as well as parts of the Zend Framework.


Requirement: 
We required a dedicated server atleast 2GB of Ram alongside Ubuntu 16.04 LTS installed LAMP Stack.
1- Nginx
root@Server16: # apt install nginx

2- PHP

root@Server16: # apt install php7.0-fpm

Other required PHP extensions:
root@Server16: # apt-get install php7.0-mysql php7.0-zip php7.0-curl php7.0-gd php7.0-intl php-pear php-imagick php7.0-imap php7.0-mcrypt php-memcache  php7.0-pspell   php7.0-recode php7.0-sqlite3 php7.0-tidy php7.0-xmlrpc php7.0-xsl php7.0-mbstring php-gettext php7.0-soap
3- MySQL
root@Server16: # apt install mysql-server

Step 1: Download as well as extract Magento

Download Magento from below mentioned URL:
root@Server16: # wget https://github.com/OpenMage/magento-mirror/archive/magento-1.9.zip
Use ascendency below to extract zip file
root@Server16: # unzip -d /var/www/html/ magento-1.9.zip
Where  

unzip                                        This is a command
-d                                              Extract file into specific directory 
/var/www/html                       Path where Zip volition live extract 

Now rename the folder alongside a uncomplicated call using the ascendency below:
root@Server16: # mv /var/www/html/magento-mirror-magento-1.9/ /var/www/html/magento 

Change Permission using ascendency below:
root@Server16: # chown -R www-data:www-data /var/www/html/magento 

Step 2: Create Server Blocks (Virtual Host) as well as enable it.

Let's configure Nginx Server block using ascendency below:

root@Server16: # vi /etc/nginx/sites-available/magento.conf

And add together the syntax below:

# Default server configuration # server {         brain 80;         brain [::]:80;          # SSL configuration         #         # brain 443 ssl default_server;         # brain [::]:443 ssl default_server;         #         # Note: You should disable gzip for SSL traffic.         # See: https://bugs.debian.org/773332         #         # Read upwards on ssl_ciphers to ensure a secure configuration.         # See: https://bugs.debian.org/765782         #         # Self signed certs generated past times the ssl-cert parcel         # Don't purpose them inwards a production server!         #         # include snippets/snakeoil.conf;          root /var/www/html/magento;          # Add index.php to the listing if y'all are using PHP         index index.php index.html index.htm index.nginx-debian.html;          server_name magento.lan;          place / {                 # First campaign to serve asking every minute file, as well as thus                 # every minute directory, as well as thus autumn dorsum to displaying a 404.                 try_files $uri $uri/ =404;         }  place   .php/ {         rewrite ^(.*.php)/ $1 last;         }           # overstep the PHP scripts to FastCGI server listening on 127.0.0.1:9000         #         place   \.php$ {                 include snippets/fastcgi-php.conf;         #         #       # With php7.0-cgi alone:         #       fastcgi_pass 127.0.0.1:9000;         #       # With php7.0-fpm:                 fastcgi_pass unix:/run/php/php7.0-fpm.sock;         }          # deny access to .htaccess files, if Apache's document root         # concurs alongside nginx's i         #         place   /\.ht {                 deny all;         } }   

Save as well as Exit from file

Now Create a link of Server blocks using ascendency below:
root@Server16: # ln -s /etc/nginx/sites-available/magento.conf /etc/nginx/sites-enabled/magento.conf

Check Nginx configuration as well as restart service:
root@Server16: # nginx -t nginx: the configuration file /etc/nginx/nginx.conf syntax is ok nginx: configuration file /etc/nginx/nginx.conf exam is successful 
Restart Nginx Using ascendency below
root@Server16: # systemctl restart nginx.service 

Step 3: Create a database as well as assign permission:

Let's Create a database as well as assign permission:
Create Database
mysql> practice database magento;
Create User
mysql> practice user magento@localhost identified past times 'magento';
Assign Perrmission
mysql> grant all privileges on magento.* to magento@'localhost' identified past times 'magento';
Reload permisson
mysql> even out privileges;

Step 4: Finish Magento Installation 

Open browser  hitting domain call as well as follow the pedagogy to complete installation process.


Accept the license agreement


Select Location, TimeZone as well as Default Currency type


Fill Database Configuration detail, Admin spider web access URL as well as session shop options


Fill Magento Admin login access details:


All set, afterwards completing all the steps y'all volition larn the window similar below.


Magento has been installed successfully, Now y'all tin get-go working alongside Admin panel using link below

http://magento.lan/index.php/admin/

And y'all Frontend volition live looking similar this 


!!!That's ALL!!!!


Sumber https://linuxhowtoguide.blogspot.com/

Sabtu, 28 Januari 2017

How To Install Lxd Container Hypervisor On Ubuntu 16.04 Lts Server

LXD Container:-
LXD is a lightweight opened upward source hypervisor, It allows yous to exercise multiple Container on a unmarried machine or Virtual machine also. Where yous tin run multiple application, services without extra toll And without modifying heart server application package. 

i.e. yous are working inwards a hosting provider or Software evolution company, Where yous demand multiple version of  PHP, MySQL too Apache etc.. but yous don't desire to modify existing installation because it tin interrupt electrical flow running application. For such requirement, yous tin exercise LXD container.

 LXD System requirement:
 One working PC amongst Ubuntu 16.04 LTS

Required Software packages:
1- LXD
2- zfsutils-linux
3- bridge-utils 


Step-1: Install LXD
root@Server16: # apt install lxd

Step-2: Install zfsutils-Linux
ZFSUtils-Linux is required to exercise ZFS file organization to shop LXD Container, for ZFS file organization nosotros tin exercise the same region or tin exercise simply about other HDD.

Use ascendance below to Install Zfsutils-linux
root@Server16: # apt install zfsutils-linux


Step-3:  Install bridge-utils
we required this packet to setup network brace interface hence that container's interface tin become IP too tin communicate amongst Public network.

Use ascendance below to install this package.
root@Server16: # apt install bridge-utils

Step-4: Create Bridge network interface.
 Modify your network Interface too it should hold off similar below.

Change your Primary network interface to Manual too bind it amongst brace network.


# This file describes the network interfaces available on your organization # too how to activate them. For to a greater extent than information, come across interfaces(5).  source /etc/network/interfaces.d/*  # The loopback network interface auto lo iface lo inet loopback  # The main network interface #auto enp0s3 iface enp0s3 inet manual # Bridge Network Interface auto br0 iface br0 inet dhcp         bridge-ports enp0s3         bridge-ifaces enp0s3 # Secondary Network Interface auto enp0s8 iface enp0s8 inet dhcp 

Save too Exit from the file.

Step-5: Restart your br0 network interface 
root@Server16: # ifdown enp0s3 && ifup enp0s3 && ifup br0

Please Note: - If yous don't come across respond from brace interface, Please restart your server once.

Check your network interface too IP address condition using ascendance below.
root@Server16: # ifconfig br0       Link encap:Ethernet  HWaddr 08:00:27:ab:3c:75           inet addr:192.168.28.120  Bcast:192.168.28.255  Mask:255.255.255.0           inet6 addr: fe80::a00:27ff:feab:3c75/64 Scope:Link           UP BROADCAST RUNNING MULTICAST  MTU:1500  Metric:1           RX packets:337 errors:0 dropped:0 overruns:0 frame:0           TX packets:141 errors:0 dropped:0 overruns:0 carrier:0           collisions:0 txqueuelen:1000           RX bytes:30299 (30.2 KB)  TX bytes:17098 (17.0 KB)  enp0s3    Link encap:Ethernet  HWaddr 08:00:27:ab:3c:75           inet6 addr: fe80::a00:27ff:feab:3c75/64 Scope:Link           UP BROADCAST RUNNING MULTICAST  MTU:1500  Metric:1           RX packets:398 errors:0 dropped:0 overruns:0 frame:0           TX packets:149 errors:0 dropped:0 overruns:0 carrier:0           collisions:0 txqueuelen:1000           RX bytes:40161 (40.1 KB)  TX bytes:17866 (17.8 KB)  enp0s8    Link encap:Ethernet  HWaddr 08:00:27:9f:86:47           inet addr:10.0.2.5  Bcast:10.0.2.255  Mask:255.255.255.0           inet6 addr: fe80::a00:27ff:fe9f:8647/64 Scope:Link           UP BROADCAST RUNNING MULTICAST  MTU:1500  Metric:1           RX packets:7 errors:0 dropped:0 overruns:0 frame:0           TX packets:15 errors:0 dropped:0 overruns:0 carrier:0           collisions:0 txqueuelen:1000           RX bytes:1988 (1.9 KB)  TX bytes:1720 (1.7 KB)  lo        Link encap:Local Loopback           inet addr:127.0.0.1  Mask:255.0.0.0           inet6 addr: ::1/128 Scope:Host           UP LOOPBACK RUNNING  MTU:65536  Metric:1           RX packets:80 errors:0 dropped:0 overruns:0 frame:0           TX packets:80 errors:0 dropped:0 overruns:0 carrier:0           collisions:0 txqueuelen:1           RX bytes:5920 (5.9 KB)  TX bytes:5920 (5.9 KB)  root@Server16: # 

Step-6: Complete LXD configuration -
During the LXD configuration wizard  It volition inquire to configure brace interface, Select No when it inquire for auto too lead no to give brace interface manually.

root@Server16: # lxd init Name of the storage backend to exercise (dir or zfs) [default=zfs]: zfs Create a novel ZFS puddle (yes/no) [default=yes]? yes Name of the novel ZFS puddle [default=lxd]: zfs-pool Would yous similar to exercise an existing block device (yes/no) [default=no]? no Size inwards GB of the novel loop device (1GB minimum) [default=15]: 10 Would yous similar LXD to last available over the network (yes/no) [default=no]? no Do yous desire to configure the LXD brace (yes/no) [default=yes]? yes Warning: Stopping lxd.service, but it tin notwithstanding last activated by:   lxd.socket LXD has been successfully configured. root@Server16: # 

Configuration exercise has been completed successfully.


Step-7: Create your showtime Container using the command below.
root@Server16: # lxc launch ubuntu:xenial C1 Creating C1 Starting C1 root@Server16: # 
 
Your showtime container is ready, let's cheque container condition using ascendance bellow.
 
root@Server16: # lxc listing +------+---------+-----------------------+------+------------+-----------+ | NAME |  STATE  |         IPV4          | IPV6 |    TYPE    | SNAPSHOTS | +------+---------+-----------------------+------+------------+-----------+ | C1   | RUNNING | 192.168.28.121 (eth0) |      | PERSISTENT | 0         | +------+---------+-----------------------+------+------------+-----------+ root@Server16: # 


!!! Congrats, You bring successfully configured LDX hypervisor !!!


**Some other useful ascendance to operate amongst LXD**

1- Command  login to LXD container:
root@Server16: # lxc exec C1 /bin/bash root@C1: # 

2- By default you can't login to container using password from a remote PC because 
"PasswordAuthentication  no" not allowed from sshd_conf file. 
Let's modify this file to access via ssh from remote pc.
 
root@C1: # vi /etc/ssh/sshd_config
And modify passwordaAthentication file similar below.

# To enable empty passwords, alter to yeah (NOT RECOMMENDED) PermitEmptyPasswords no  # Change to yeah to enable challenge-response passwords (beware issues amongst # simply about PAM modules too threads) ChallengeResponseAuthentication no  # Change to no to disable tunnelled clear text passwords PasswordAuthentication yes  # Kerberos options #KerberosAuthentication no #KerberosGetAFSToken no #KerberosOrLocalPasswd yeah #KerberosTicketCleanup yeah  

Save file too restart ssh service.
root@C1: # /etc/init.d/ssh restart [ ok ] Restarting ssh (via systemctl): ssh.service.  


Sumber https://linuxhowtoguide.blogspot.com/